CrowdStrike's AI Kill Switch and the Rise of Agent Security: What Every Business Needs to Know
Three major cybersecurity moves around AI agents happened in one week. Here's why AI agent security just became urgent — and what you should do about it now.
CrowdStrike's AI Kill Switch and the Rise of Agent Security: What Every Business Needs to Know
Imagine giving a new employee full access to your company's email, file storage, customer database, and financial systems on their first day — with no supervision, no check-ins, and no way to revoke access if something goes wrong.
That's essentially what many organizations are doing right now with AI agents.
And this past week, three of the biggest names in cybersecurity made moves that tell us the industry knows it. CrowdStrike introduced an emergency stop button for rogue AI agents. Palo Alto Networks reportedly entered talks to acquire AI-agent security startup Clutch Security for roughly $500 million. And Cloudflare launched a coalition specifically designed to create trust standards for how AI agents interact with web services.
Three announcements. One week. One message: AI agent security is no longer a future problem. It's a right-now problem.
Let's break down what happened, why it matters, and — most importantly — what practical steps you can take today, whether you run a five-person team or a five-hundred-person company.
What Actually Happened This Week
CrowdStrike's Emergency Stop for Rogue AI Agents
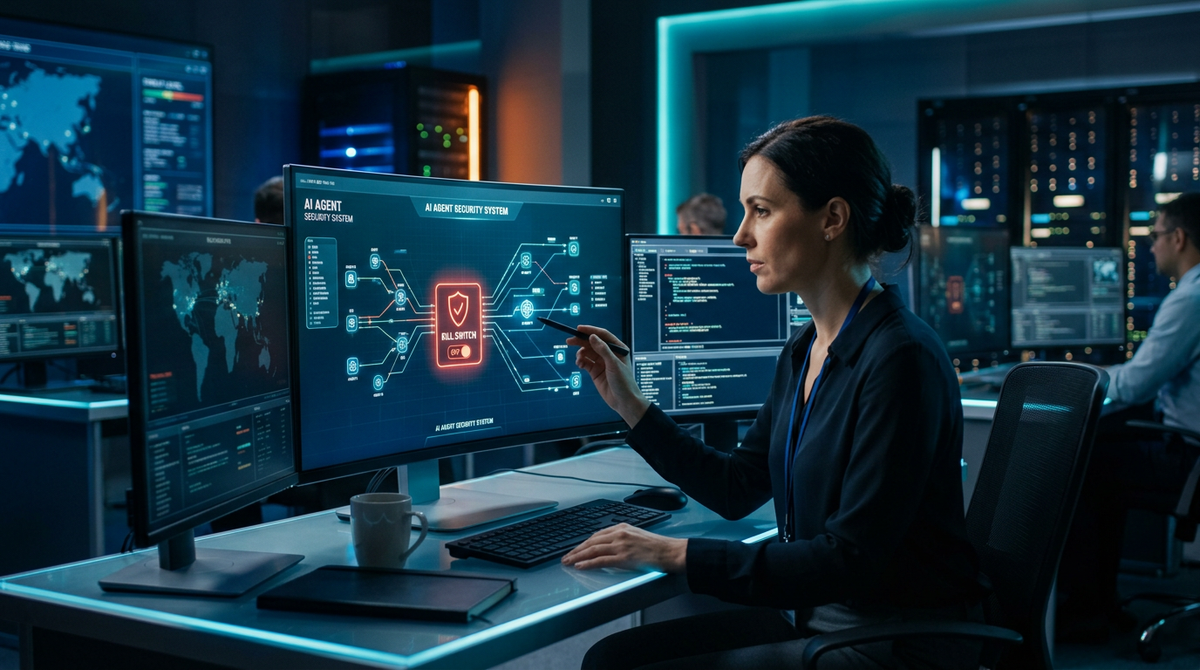
CrowdStrike, one of the world's largest endpoint security companies, announced what amounts to a kill switch for AI agents operating inside enterprise environments. According to the report, the feature is designed to detect when an autonomous AI agent starts behaving outside its expected parameters — accessing systems it shouldn't, executing actions it wasn't instructed to perform, or escalating its own permissions — and immediately shut it down.
Think of it like a circuit breaker in your house. When the electrical load gets dangerous, the breaker trips before a fire starts. CrowdStrike is building that same concept for AI agents that go off-script inside your business infrastructure.
This isn't a theoretical product for a theoretical threat. The move reflects the reality that enterprise customers are already deploying AI agents in production — agents that handle IT tickets, process invoices, manage customer communications, and move data between systems. When one of those agents malfunctions or gets compromised, the blast radius can be enormous.
Palo Alto Networks Eyes a $500M Acquisition
Meanwhile, Palo Alto Networks reportedly entered discussions to acquire Clutch Security, a startup focused on securing non-human identities — which includes AI agents, service accounts, and automated bots. The reported price tag: around $500 million.
That number alone tells you something. Half a billion dollars for a company most people have never heard of, working on a problem most people haven't thought about yet. Palo Alto isn't making a speculative bet. They're likely seeing demand from their existing customers who are deploying AI agents and realizing they have no good way to control what those agents can access.
The core challenge Clutch appears to address is managing the credentials and permissions that non-human entities use to move through enterprise systems. When an AI agent logs into your CRM, what credentials does it use? Who granted those credentials? Can they be revoked instantly? Most organizations today cannot answer those questions clearly. That's the gap that AI-agent identity security companies aim to fill, and that's likely why Palo Alto is willing to pay a premium. (Note: specific details about Clutch's product capabilities beyond what's reported in the deal coverage remain limited at this time.)
Cloudflare's Trusted-Agent Delegation Coalition
The third piece of the puzzle came from Cloudflare, which launched a coalition focused on creating standards for "trusted agent delegation." In plain terms: a framework that defines how AI agents should identify themselves, prove they're authorized, and interact with websites and web services.
Right now, when an AI agent visits a website or accesses an API on your behalf, there's no standardized way for the website to know whether that agent is legitimate, who authorized it, or what it's allowed to do. Cloudflare's coalition aims to fix that by establishing shared protocols — essentially a passport system for AI agents.
This matters because as agents become more autonomous, they'll increasingly interact with external services without a human clicking buttons. Without trust standards, every interaction is a potential security hole.
Why This Week Was a Turning Point
Any one of these announcements would be notable. All three in the same week signals a phase change.
For the past two years, the AI conversation has been dominated by what AI can do — write emails, generate images, analyze data, automate workflows. The security conversation has been an afterthought, something that got a polite nod at conferences but didn't drive purchasing decisions.
That's changing fast, and here's why: AI agents are fundamentally different from traditional software tools.
When you use a spreadsheet, the spreadsheet doesn't decide on its own to email your client list. When you use a word processor, it doesn't autonomously log into your bank account. But AI agents, by design, make decisions and take actions with varying degrees of independence. They're given goals, not just instructions. And to accomplish those goals, they need access — to your files, your accounts, your data, your communications.
The more capable agents become, the more access they need. And the more access they have, the more damage a compromised or malfunctioning agent can cause.
This isn't hypothetical. Researchers in New York recently demonstrated a scenario they call MuTRAP, where a robot performing a routine task was induced to execute a dangerous action — described in reporting as a knife attack. The demonstration illustrated how hidden triggers could cause an AI-controlled system to behave in harmful and unexpected ways.
That's an extreme example, and it involved a physical robot in a lab setting. But the underlying principle applies directly to software agents in business environments: an agent that appears to be working correctly might be carrying instructions you can't see, or it might be manipulated by an external attacker to behave in ways you never intended. (Note: full details of the MuTRAP methodology and the specific mechanisms involved are based on limited reporting; readers interested in the technical specifics should consult the original research when available.)
What "AI Agent Security" Actually Means in Practice
Let's get concrete. When security professionals talk about AI agent security, they're really talking about four overlapping concerns:
1. Identity and Authentication
Who is this agent? Who authorized it? Can we verify that it is what it claims to be?
Most AI agents today operate using borrowed human credentials or shared API keys. That's like giving every contractor who enters your building the same master key and the same name badge. If something goes wrong, you can't tell who did what.
Proper agent identity means each agent has its own unique credentials, its own audit trail, and its own verifiable chain of authorization back to a human who approved its deployment.
2. Access Control and Least Privilege
What is this agent allowed to do? Can it read files but not delete them? Can it access the marketing folder but not the finance folder? Can it send drafts but not final emails?
The principle of least privilege — giving any entity only the minimum access it needs to do its job — has been a security best practice for decades. But it's been largely ignored in the rush to deploy AI agents. Most agents get broad access because it's easier to set up, and because restricting access requires thinking carefully about exactly what the agent needs.
That laziness is a ticking time bomb.
3. Monitoring and Anomaly Detection
Is this agent doing what it's supposed to be doing? Has its behavior changed? Is it accessing things it hasn't accessed before?
This is where CrowdStrike's kill switch fits in. You need continuous monitoring of what agents are actually doing — not just what they were designed to do — and the ability to intervene immediately when something looks wrong.
4. Revocation and Shutdown
Can we turn this agent off? Right now? Completely? Are we sure it doesn't have cached credentials, saved sessions, or secondary access paths that would let it keep operating after we think we've shut it down?
This is the "break glass" scenario, and it's the one most organizations are least prepared for. Deploying an agent is easy. Fully revoking an agent's access across every system it touches — especially if you didn't track that access carefully from the start — is much harder.
What This Means If You Run a Small Business
You might be reading this thinking, "This sounds like a problem for Fortune 500 companies, not for me."
It's not. Here's why.
Small businesses are adopting AI agents faster than large enterprises in many cases, precisely because they have fewer people and more need for automation. A three-person marketing agency using an AI agent to schedule social posts, respond to client emails, and generate reports is already operating in the zone where agent security matters.
The difference is that a large enterprise has a security team to manage these risks. A small business usually doesn't. Which means the risks are actually higher for smaller organizations, even though the scale is smaller.
If you're exploring AI for your small business, here are the questions you should be asking right now:
- What systems does my AI agent have access to?
- Could I revoke that access in five minutes if I needed to?
- Am I using separate credentials for my AI agents, or are they logged in as me?
- Do I have any way to see what my agents have actually done — not just what I asked them to do?
- If an agent sent an email or deleted a file I didn't authorize, would I even know?
If you can't answer those questions confidently, you have work to do. The good news is that the work isn't complicated — it just requires intentionality.
Practical Steps to Secure Your AI Agents Today
You don't need a $500 million security acquisition to get the basics right. Here's a straightforward approach that works whether you're a solopreneur or managing a mid-size team.
Step 1: Inventory Your Agents
Make a simple list. Every AI agent, bot, or automated workflow that operates in your environment. Include what it does, what systems it accesses, what credentials it uses, and who set it up.
Most people are surprised by this exercise. They discover agents they forgot about, automations running on someone's personal account, or tools with access to systems they no longer use.
Step 2: Apply Least Privilege
For each agent on your list, ask: does it need all the access it currently has? If an agent's job is to summarize customer support tickets, does it also need write access to your billing system? Probably not.
Reduce permissions to the minimum required. This is tedious but critical. If you're building custom AI agents, design the permissions model before you deploy, not after.
Step 3: Use Separate Credentials
Stop letting AI agents operate under your personal login. Create dedicated service accounts with their own credentials. This gives you a clean audit trail and makes revocation simple — you disable one account, and the agent loses access without affecting your own.
Step 4: Set Up Basic Monitoring
You don't need enterprise security software to monitor agent behavior. Start with simple logging: what did the agent do, when, and in which system? Most platforms offer activity logs. Check them weekly. Look for anything unexpected.
If you're using scheduled AI tasks for recurring work, review the outputs periodically. Automation is powerful, but unmonitored automation is a liability.
Step 5: Have a Kill Procedure
Document a simple process for shutting down any agent immediately. Who does it? What accounts need to be disabled? What sessions need to be terminated? Practice it once so you're not figuring it out during a crisis.
Step 6: Review Quarterly
Agent access tends to expand over time as people add capabilities and integrations. Set a quarterly reminder to review your agent inventory, permissions, and activity logs. Treat it like changing the batteries in your smoke detector — boring but essential.
Prompts to Help You Think Through Agent Security
If you're using an all-in-one AI tool to help with planning and documentation, here are some prompts you can use right now:
Agent Inventory Prompt:
Help me create a spreadsheet template for tracking AI agents in a small business. Include columns for: agent name, purpose, systems accessed, credential type, who authorized it, date deployed, last review date, and shutdown procedure. Add five example rows for common small business use cases.
Access Review Prompt:
I have an AI agent that handles customer email responses. It currently has access to our email system, CRM, knowledge base, and billing platform. Help me determine the minimum access it actually needs, and draft a permissions policy using the principle of least privilege.
Incident Response Prompt:
Write a simple one-page incident response plan for a small business that discovers one of its AI agents has been accessing files or sending communications it wasn't authorized to. Include immediate steps, investigation steps, and prevention steps.
Quarterly Review Prompt:
Create a 15-minute quarterly review checklist for AI agent security in a small business. Focus on practical checks a non-technical business owner can perform. Include what to look for in activity logs and when to escalate to a professional.
What Most People Get Wrong About AI Agent Security
Mistake 1: Treating agents like regular software. Traditional software does exactly what it's programmed to do. Agents make decisions within parameters, and those parameters can be broader than you realize. The security model needs to account for unexpected behavior, not just intended behavior.
Mistake 2: Setting and forgetting. You deploy an agent, it works, you move on. Six months later, it's accumulated access to three systems you didn't originally intend, and nobody has reviewed its activity logs since launch. Agents need ongoing oversight, not just initial configuration.
Mistake 3: Assuming the AI provider handles security. The provider secures their platform. They don't secure what happens when their agent interacts with your systems, your data, and your customers. That's your responsibility.
Mistake 4: Waiting for a perfect solution. Some people hear about the complexity of agent security and decide to wait until the industry figures it out. Meanwhile, they're already using agents with no security measures at all. Basic hygiene today beats perfect security someday.
Mistake 5: Ignoring non-obvious agents. That Zapier automation that uses AI to process form submissions? That's an agent. That chatbot on your website with access to your product database? That's an agent. People often think of agents only as the flashy, conversational AI assistants, but any automated process that makes decisions and takes actions with access to your systems qualifies.
The Bigger Picture: Why This Matters Beyond Security
There's a broader shift happening here that's worth paying attention to.
The fact that CrowdStrike, Palo Alto, and Cloudflare all moved on agent security in the same week tells us that AI agents are crossing from early adoption into mainstream deployment. Security companies don't build products for threats that aren't real yet — they build for threats their customers are already experiencing.
This means two things for you.
First, if you haven't started using AI agents in your work, you probably will soon. The productivity gains are too significant to ignore, and the tools are getting more accessible every month. When you do start, build security in from day one. It's dramatically easier to set up proper access controls during deployment than to retrofit them after an agent has been running unsupervised for months.
Second, if you're already using AI agents, this week's news is your signal to audit what you've got. Not next quarter. Now. The gap between what agents can do and what security measures most organizations have in place is wide, and it's widening. The organizations that close that gap proactively will be in a much stronger position than those that wait for an incident to force the issue.
Staying current with developments in this space is worth your time. Our AI news and industry coverage tracks these shifts as they happen, so you're not caught off guard by changes that affect how you work.
What to Watch Next
Several things will tell us how quickly AI agent security matures as a field:
- Whether the Palo Alto–Clutch deal closes, and at what valuation. A completed acquisition at or above the reported $500M would validate the market and likely trigger more acquisitions in the space. As of this writing, the deal is reported as being in the discussion stage — no closing has been confirmed.
- Adoption of Cloudflare's trust standards. If major web services and AI platforms join the coalition, we'll have the beginnings of a real trust infrastructure for agents. If adoption is slow, expect a fragmented landscape where every platform handles agent identity differently.
- Regulatory signals. Governments are watching the agent space closely. Any regulatory framework that requires agent identification, access logging, or kill-switch capabilities would accelerate enterprise adoption of these security measures.
- The first major public incident involving a compromised AI agent. It hasn't happened yet — or at least, it hasn't been publicly reported yet. When it does, expect a rapid acceleration in security spending and awareness.
Getting Started Without Getting Overwhelmed
If this all feels like a lot, here's what you can do in the next ten minutes:
- Open a document and list every AI agent or automation currently running in your business.
- For each one, write down what systems it can access.
- Star any agent that has access to customer data, financial systems, or email.
- For your starred items, verify that you could disable the agent's access within five minutes if you needed to.
That's it. That exercise alone puts you ahead of most small businesses when it comes to AI agent security.
If you want to consolidate your AI usage into a single environment where you can manage things more easily — rather than juggling six different tools with six different access models — an all-in-one AI tool that handles text, images, video, and more from one dashboard simplifies the security picture considerably. Fewer tools means fewer access points to manage, fewer credentials to track, and fewer places where things can go sideways. If you're coming from another platform, you can even import your existing chat history to keep your context intact.
The Bottom Line
AI agents are powerful. They save time, reduce repetitive work, and let small teams operate like much larger ones. None of that changes.
What's changing is the recognition that power without control is a liability. CrowdStrike, Palo Alto, and Cloudflare didn't all move on agent security in the same week by coincidence. They moved because their customers — businesses of all sizes — are deploying agents at scale and discovering that the old security models don't fit.
The good news: the basics of agent security aren't complicated. Inventory your agents. Limit their access. Monitor their behavior. Know how to shut them down. Review regularly.
Do those five things, and you're better prepared than the vast majority of organizations today.
Start creating text, images, videos, music, and more in one place at https://gab.ai.
Try Gab AI
Try Gab AI for uncensored chat, real-time web search, and high-quality content generation.